Defender Self-Encrypting Internal Secure SEDs FOR SALE – Kanguru Defender® SED Self-Encrypting Drives – Opal-Compliant, Hardware-Based, Internal Self-Encrypting SEDs – Self encrypting internal secure ssds opal sed hardware based solid state drives
Defender Self-Encrypting Internal Secure SEDs
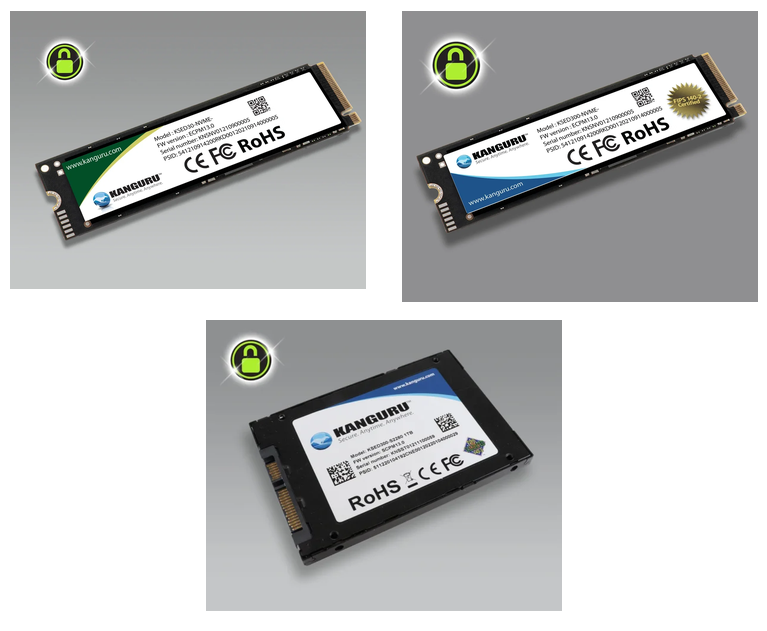
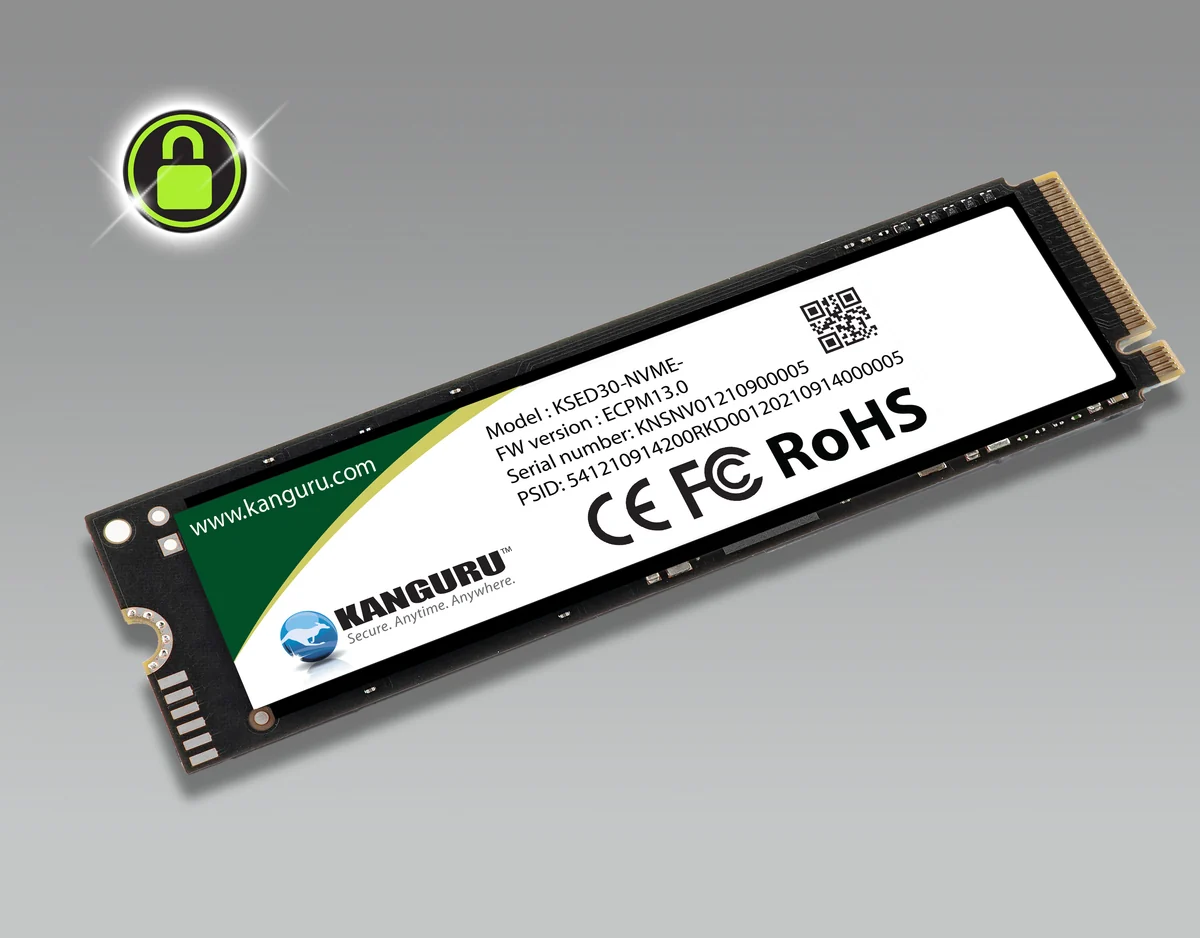
- Kanguru Defender® SED30™ NVMe SSD
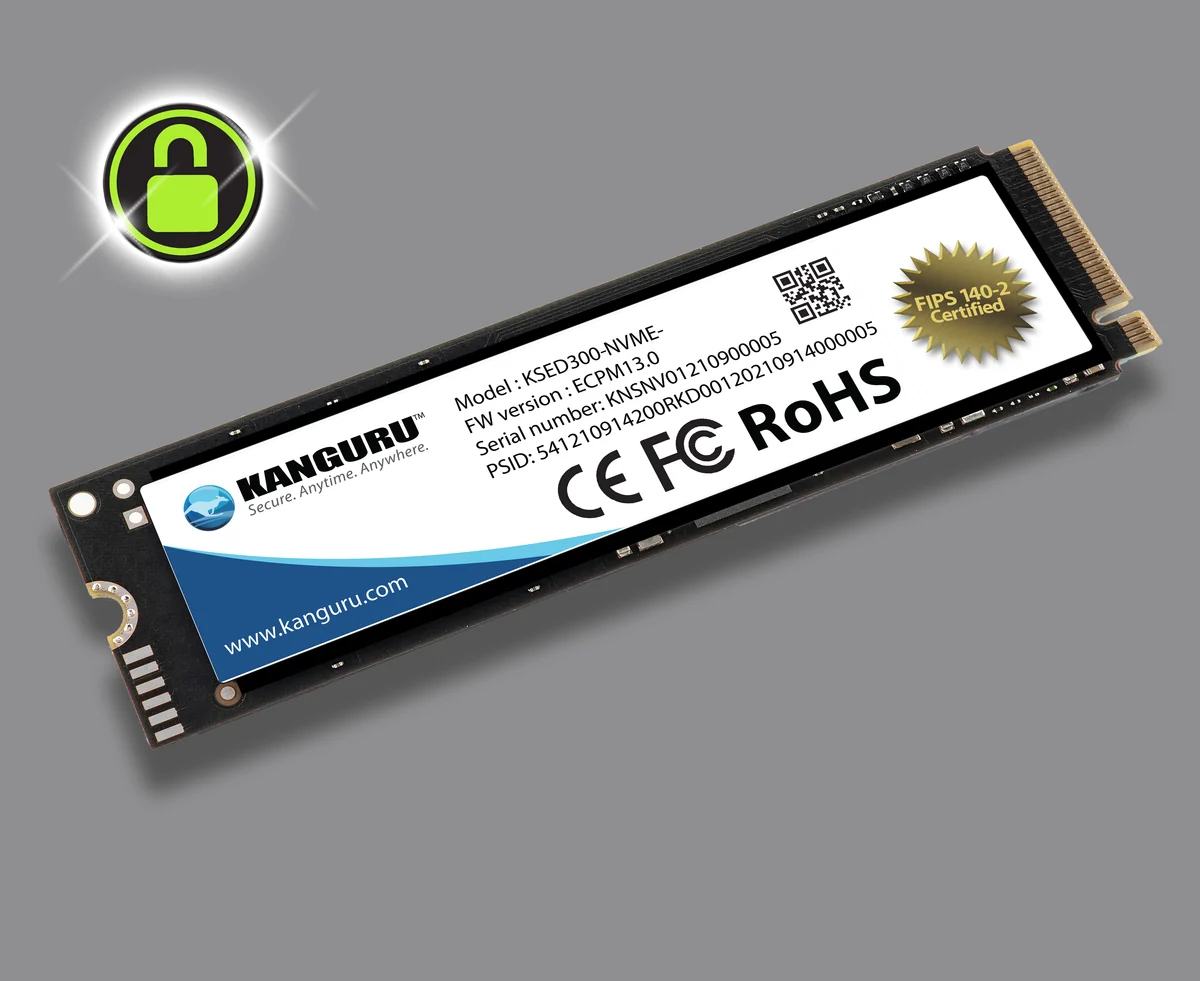
- Kanguru Defender® SED300™ NVMe SSD FIPS 140-2 Certified
- Kanguru Defender® SED300™ SATA SSD FIPS 140-2 Certified
Defender Self-Encrypting Internal Secure SEDs
Defender Self-Encrypting Internal Secure SEDs for sale – Kanguru Defender® SED Self-Encrypting Drives – Opal-Compliant, Hardware-Based, Internal Self-Encrypting SEDs – Self encrypting internal secure ssds opal sed hardware based solid state drives
Defender Self-Encrypting Internal Secure SEDs are hardware-based self-encrypting solid state drives designed to help organizations protect sensitive data stored on laptops, tablets, desktops, and other compatible computers. Kanguru Defender® SEDs combine high-performance solid-state storage with hardware-based AES 256-bit encryption, Opal compliance, and secure pre-boot authentication.
Organizations looking to Buy Defender Self-Encrypting Internal Secure SEDs can choose Kanguru Defender® SED solutions for protecting data at rest without relying exclusively on software-based disk encryption. Select models are FIPS 140-2 certified and designed for environments that require enhanced hardware security, centralized provisioning, and strong protection for stored information.
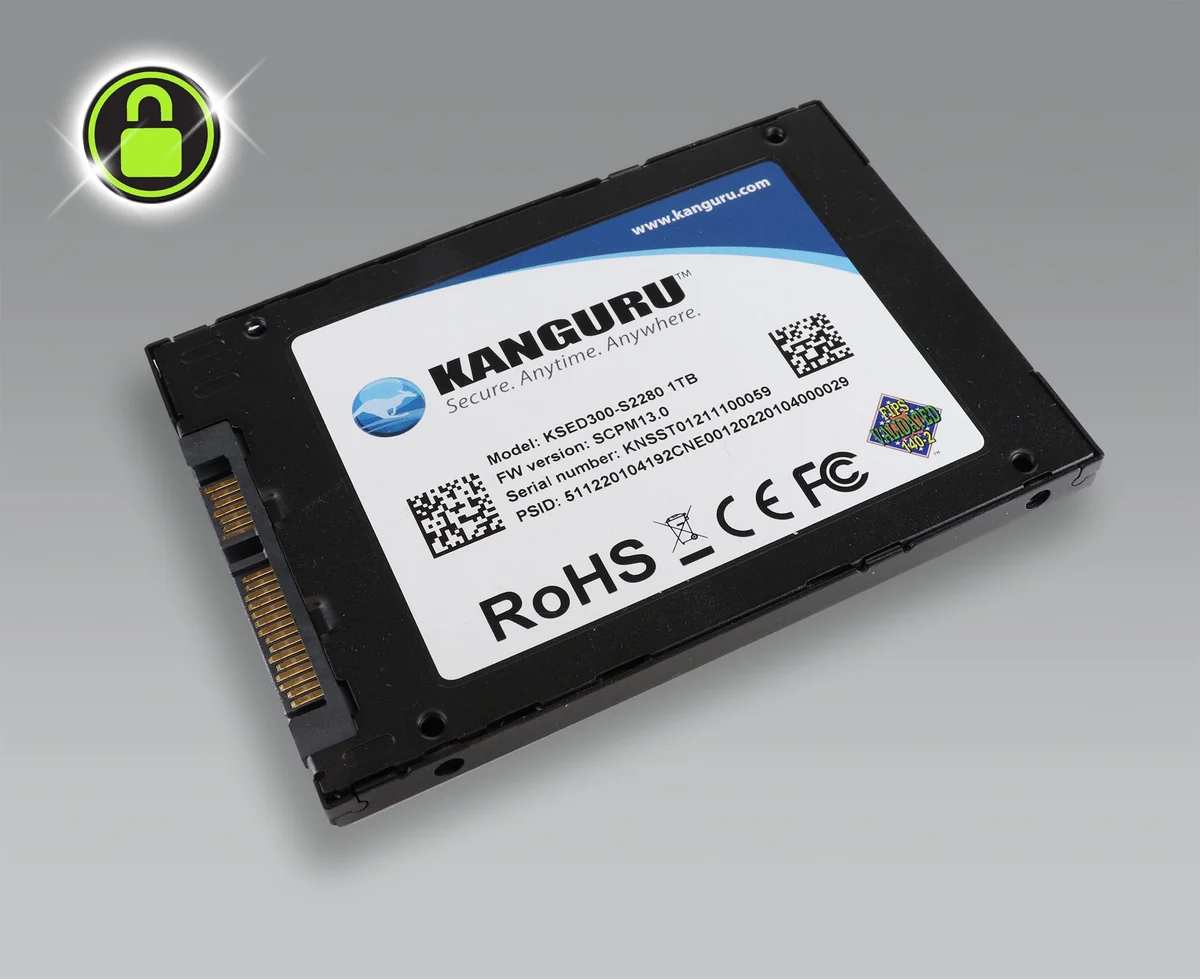
Buy Defender Self-Encrypting Internal Secure SEDs
Buy Defender Self-Encrypting Internal Secure SEDs from AFT India for hardware-based data protection and secure storage applications. Kanguru Defender SEDs are designed for organizations that need self-encrypting internal SSDs with full-drive hardware encryption, secure pre-boot authentication, and Opal-compliant security features.
These Defender Self-Encrypting Internal Secure SEDs provide a security-focused storage solution for business computers, enterprise laptops, tablets, workstations, and other systems where protecting sensitive data at rest is essential.
Kanguru Defender® SED Self-Encrypting Drives
Kanguru Defender® SED Self-Encrypting Drives are Opal-compliant, hardware-based internal self-encrypting SEDs engineered to protect information stored on the drive. The encryption is performed by dedicated hardware rather than depending solely on the host operating system or application software.
Key security and performance features include:
- AES 256-bit hardware encryption
- Hardware-based full-drive encryption
- Opal-compliant self-encrypting drive technology
- Secure pre-boot password authentication
- On-board Pre-Boot Authentication (PBA)
- Automatic drive locking when powered off
- High-performance solid-state storage
- FIPS 140-2 certified models available
- TAA-compliant options
- Provisioning with the Kanguru Opal Commander
Hardware-Based Self-Encrypting Internal SSDs
Defender Self-Encrypting Internal Secure SEDs use dedicated hardware-based encryption to protect the entire storage device. Unlike approaches that encrypt selected files or folders, full-drive encryption is applied across the drive, helping protect stored information including the operating system and user data.
The integrated encryption architecture is designed to provide transparent security while maintaining normal SSD operation after authorized authentication. Once the drive has been successfully unlocked, the Kanguru Defender SED operates like a standard solid state drive.
AES 256-Bit Hardware Encryption
Kanguru Defender SEDs use AES 256-bit hardware encryption to protect data stored on the drive. Encryption is handled by dedicated hardware within the self-encrypting drive, providing a hardware-based approach to protecting data at rest.
When the computer is powered down, the Defender SED automatically locks itself. The data stored on the drive, including the operating system, becomes inaccessible until an authorized authentication process unlocks the drive.
Secure Pre-Boot Password Authentication
Defender Self-Encrypting Internal Secure SEDs incorporate a secure pre-boot authentication environment. The on-board Pre-Boot Authenticator (PBA) enables an authorized user to authenticate before access to the encrypted drive is permitted.
After successful authentication, the drive is unlocked and functions normally, allowing the operating system and applications to access the stored data.
Full Disk Hardware Encryption for Data at Rest
Protecting data at rest is a critical requirement for organizations storing confidential business information on endpoint devices. Defender Self-Encrypting Internal Secure SEDs provide full-drive hardware encryption intended to protect information when a computer or storage device is powered off.
Because encryption is implemented at the drive hardware level, the security mechanism operates independently of individual files and folders. This makes Kanguru Defender SEDs suitable for organizations seeking hardware-based protection for stored data across compatible computing platforms.
Kanguru Opal Commander Provisioning Tool
The Kanguru Opal Commander provides a provisioning and management tool for Kanguru Defender SED deployments. It is designed to assist with configuring Defender self-encrypting drives and supporting hardware-based encryption across system rollouts.
For organizations deploying multiple Defender Self-Encrypting Internal Secure SEDs, the Opal Commander provides a dedicated approach to provisioning drives equipped with an on-board hardware encryption processor.
FIPS 140-2 Certified Defender SED Models
Select Kanguru Defender SED models are FIPS 140-2 certified, providing an option for organizations that require certified cryptographic security hardware. Availability and certification status depend on the specific Defender SED model.
Organizations with regulatory, government, enterprise, or contractual security requirements should select the appropriate certified model based on their deployment requirements and applicable compliance standards.
Opal-Compliant Internal Self-Encrypting SEDs
Kanguru Defender SEDs are designed around Opal-compliant self-encrypting drive technology. These internal SEDs combine solid-state performance with hardware-based encryption and authentication capabilities for endpoint data protection.
Defender Self-Encrypting Internal Secure SEDs can be considered for laptops, tablets, desktops, workstations, and other compatible computers where organizations need an internal encrypted SSD solution.
Key Benefits of Defender Self-Encrypting Internal Secure SEDs
- Hardware-Based Encryption: Encryption is performed by dedicated hardware within the drive.
- AES 256-Bit Security: Protect stored data using AES 256-bit hardware encryption.
- Full-Drive Protection: Encryption applies to the entire drive rather than selected files or folders.
- Automatic Locking: The drive automatically locks when the system is powered off.
- Pre-Boot Authentication: Authorized users authenticate before the encrypted drive can be accessed.
- Opal Compliance: Designed for use with Opal-compliant self-encrypting drive environments.
- FIPS 140-2 Models: Select models provide FIPS 140-2 certified security.
- High Performance: Combines SSD storage performance with hardware-based encryption.
- Enterprise Provisioning: Kanguru Opal Commander supports provisioning for system deployments.
- Internal SSD Form Factor: Designed as an internal self-encrypting storage solution for compatible systems.
Defender Self-Encrypting Internal Secure SEDs for Business and Enterprise
Defender Self-Encrypting Internal Secure SEDs are designed for organizations that need to secure sensitive information stored on endpoint computers. They can support data-at-rest protection strategies for business systems, enterprise endpoints, government-related deployments, and other environments where hardware-based storage encryption is required.
The combination of AES 256-bit hardware encryption, secure pre-boot authentication, automatic locking, Opal compliance, and optional FIPS 140-2 certification makes Kanguru Defender SED technology suitable for security-conscious storage deployments.
Why Choose Kanguru Defender SEDs?
Kanguru Defender® SEDs integrate storage and hardware-based encryption into a single internal solid-state drive. Instead of adding encryption as a separate software layer, the Defender SED incorporates a dedicated hardware encryption processor into the drive architecture.
This approach enables organizations to deploy Defender Self-Encrypting Internal Secure SEDs for protecting data at rest while retaining the familiar functionality of an internal SSD after authorized authentication.
Buy Kanguru Defender SED Self-Encrypting Drives
If you need to Buy Defender Self-Encrypting Internal Secure SEDs, AFT India can help identify the appropriate Kanguru Defender® SED model based on your storage, encryption, compliance, interface, deployment, and quantity requirements.
Contact AFT India for product availability, model selection, enterprise quantities, FIPS 140-2 certified options, Opal-compliant SED requirements, and deployment assistance.
Defender Self-Encrypting Internal Secure SEDs – Product Highlights
| Feature | Defender SED |
|---|---|
| Drive Type | Internal Self-Encrypting Solid State Drive |
| Encryption | AES 256-bit Hardware Encryption |
| Encryption Type | Hardware-Based Full-Drive Encryption |
| Authentication | Secure Pre-Boot Password Authentication |
| PBA | On-Board Pre-Boot Authenticator |
| Drive Locking | Automatic Locking When Powered Off |
| Compliance | Opal-Compliant |
| Certification | FIPS 140-2 Certified Models Available |
| Provisioning | Kanguru Opal Commander |
| Performance | High-Performance SSD Storage |
| Application | Laptops, Tablets, Desktops, Workstations and Compatible Computers |
Frequently Asked Questions
What are Defender Self-Encrypting Internal Secure SEDs?
Defender Self-Encrypting Internal Secure SEDs are internal solid-state drives that use dedicated hardware to encrypt data stored on the drive. Kanguru Defender SEDs are designed to provide full-drive data-at-rest protection with AES 256-bit hardware encryption and secure pre-boot authentication.
How does a Kanguru Defender SED protect data?
A Kanguru Defender SED uses hardware-based encryption across the drive. When the computer is powered off, the drive automatically locks, making the stored data inaccessible until the authorized authentication process unlocks the drive.
Do Defender SEDs use AES 256-bit encryption?
Yes. Kanguru Defender SEDs use AES 256-bit hardware encryption to protect information stored on the drive.
Are Kanguru Defender SEDs FIPS certified?
Select Kanguru Defender SED models are FIPS 140-2 certified. Certification depends on the specific model, so the applicable model should be verified for deployments requiring FIPS certification.
What is the Kanguru Opal Commander?
Kanguru Opal Commander is a provisioning tool designed to assist with configuring and deploying Kanguru Defender SEDs. It works with the drive’s dedicated hardware encryption architecture for system rollouts.
Where can I Buy Defender Self-Encrypting Internal Secure SEDs?
You can Buy Defender Self-Encrypting Internal Secure SEDs from AFT India. Contact AFT India for current availability, compatible models, enterprise quantities, and requirements for Opal-compliant or FIPS 140-2 certified self-encrypting drives.
Buy Defender Self-Encrypting Internal Secure SEDs
Buy Defender Self-Encrypting Internal Secure SEDs from Aft india for sale.